Digital Defence: Securing Your Retail Ecosystem
Retailers depend on connected systems to take payments, update stock, manage staff access and serve customers across several channels. Each connection creates a potential entry point for fraud, data theft or disruption. Effective digital defence starts with knowing which systems hold sensitive information, then applying controls that reduce exposure without slowing everyday work. The following steps will help you secure the full retail ecosystem, from ecommerce platforms to tills and back-office tools.
Mapping Your Retail Digital Footprint
Create an inventory of every website, app, device, user account and third-party service connected to your retail operation. Include forgotten test sites, former employees’ accounts, marketplace integrations and store devices that access shared networks, all of which could be vulnerable to online shopping scams. Digital footprint mapping can reveal overlooked assets that attackers may find before your team does.
Record who owns each system, what data it holds and when its access was last reviewed. Harvard’s digital footprint guidance also recommends limiting the personal and operational information available online. Repeat this audit quarterly and whenever you open a location, launch a sales channel or change suppliers.
Protecting Online and Hybrid Storefronts
Keep ecommerce software, plug-ins and integrations updated, with automatic security patches enabled where possible. Remove extensions that no longer support a clear business need. A promotional plug-in left untouched after a seasonal campaign can become an avoidable route into customer accounts.
For connected sales channels, choose a retail POS system that brings online, in-person and hybrid payment activity together while supporting inventory and employee tracking. Central visibility helps teams spot unusual patterns, such as repeated refunds across two locations or a sudden mismatch between web orders and available stock. Test offline transaction functions in advance so staff know how to respond during an internet outage.
Key Security Features of a Modern Retail POS System
Look for encryption that protects payment information while it moves between the checkout, processor and issuing institution. Tokenisation provides another safeguard by replacing sensitive details with a non-sensitive reference value. The original information then remains outside the retailer’s everyday systems.
Access controls should let managers give each employee only the permissions required for their role. A sales assistant may process purchases while refunds, price overrides and reporting remain restricted to supervisors. Audit logs should record logins, changes and transactions with clear timestamps. Ask providers how updates are delivered, how suspicious activity is flagged and how quickly support teams respond to a security incident.
Safeguarding Inventory and Employee Data
Inventory records can expose sales volumes, delivery schedules and high-value stock locations. Limit access to employees who need that information, then set alerts for bulk adjustments, unusual transfers and repeated write-offs. Reconcile physical stock with system records regularly, particularly after busy trading periods.
Employee data needs the same care. Store payroll details, contact information and performance records in approved systems with controlled access. Delete duplicate spreadsheets and remove former employees promptly from scheduling, email and till accounts. Set a documented retention period for each data category so records aren’t kept indefinitely. When sharing information with accountants or software providers, confirm who can view it and how files are protected.
Implementing Multi-Layered Security Protocols
Use several overlapping controls so one mistake doesn’t expose the whole operation. Require multi-factor authentication for administration, payment, email and stock management accounts. Separate guest Wi-Fi from networks used by tills and business devices, then encrypt backups and test that you can restore them.
Staff training should use situations they may actually face. Show employees how to check unexpected password-reset messages, report unfamiliar login prompts and verify requests to change supplier payment details. Run short refreshers throughout the year and give staff one clear reporting route.
Assign responsibility for reviewing alerts and supplier access. A documented response plan should identify who disconnects affected systems, who contacts service providers and how stores continue trading. Test that plan with a simulated checkout outage, recording any delays before the next exercise.
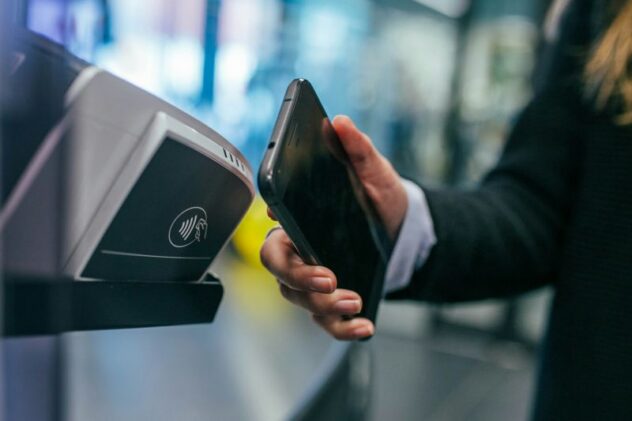
Photo by Jonas Leupe on Unsplash